ASOS Shock: Mysterious ‘Hack’ Alert Sparks Panic Among Shoppers—What’s Really Going On?
So, picture this: you’re casually scrolling through your phone, maybe hunting for the hottest new threads on ASOS, when—bam!—your screen flashes a sinister “ASOS HACKED” message that’d give you a mini heart attack faster than you can say “checkout.” Suddenly, the fashion retailer isn’t just about last season’s styles; it’s center stage in a cyber thriller that has shoppers buzzing, panicking, and, of course, racing straight to social media for answers. Now, here’s a question to chew on: if hackers can hijack your favorite app’s notification system, what’s next—your toaster threatening to leak your internet search history? While ASOS rushes to reassure us their payment info and passwords are safe (phew!), the whole ordeal shines a harsh spotlight on how vulnerable our digital lives really are. Ready to dive into the drama, the details, and what you can do to keep your data tucked safely away?
ASOS has officially responded to reports of a ‘hack’ message after shoppers received a sudden chilling alert to their mobile phones.
A message appeared on the screens of users of the mobile application which read ‘ASOS HACKED’ on Tuesday morning (6 October).
It then appeared to go on to threaten the owners of the app over a possible ‘leak’ but left users bewildered and rushing to social media.
The alert raised security concerns about the app and site being hacked and what that meant for shoppers and their data.
The message went on to read: “Dear ASOS DPO and IT, we have fully compromised the snowflake instance. Engage with us or we will leak it.”
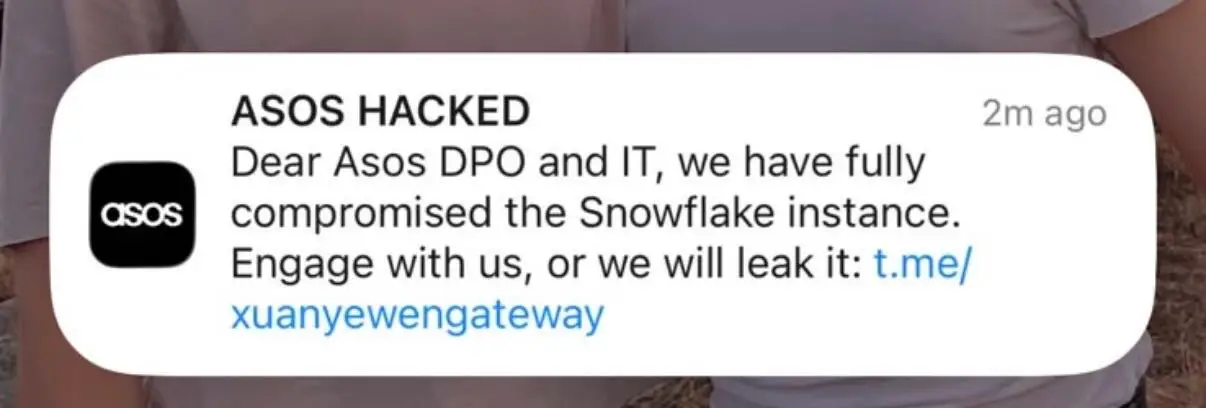
The ASOS message suddenly popped up (LADbible)
LADbible clicked the link which invited users of Telegram to a closed group called the Xuanye group gateway, which had 316 subscribers at the time of writing.
Tech experts have since responded to the alert, outlining exactly what it could mean for shoppers and how they can protect themselves.
This includes app users making sure they are using ‘randomly-generated, long, unique passwords’ for all different accounts and backing up important data.
The alert had been sent out via a push notification which was delivered to phone users that have the app downloaded, sparking concern on social media.
DPO, referenced directly in the message, is understood to refer to the data protection officer, the appointed person in a company who takes responsibility for safeguarding the data and information of customers. Snowflake meanwhile is an online data platform used by various companies.
ASOS app users got the notification (JUSTIN TALLIS/AFP via Getty Images)
ASOS addresses ‘hack’ message
ASOS have now issued a full statement on the hack reports. The fashion retailer does not believe payment-card information or passwords were impacted when a phone alert saying the company has been hacked was sent out to its millions of customers.
In a statement released through the London Stock Exchange, the company said: “Asos can confirm that, at around 10am today, an unauthorised customer notification was sent to Asos customers.
“We are investigating unauthorised activity involving third-party platforms that we use to communicate with customers. We took immediate action to restrict access to the notification platforms and are working with our internal and external specialist advisers, as well as all relevant authorities.
“Basic personal information including name and contact details may have been accessed.
“We do not believe that payment-card information or account passwords, were impacted.
“Our website and app are operating as normal, with no current disruption to any aspects of our operations.
“Customer trust is incredibly important to us, and if the situation changes an update will be provided as appropriate.
“The Company has cyber security insurance with a large global provider, including business continuity insurance. It is too early to quantify any potential impact on trading.”
“This is an unusually brazen message”
Marijus Briedis, Chief Technology Officer at NordVPN, has described the alert as ‘unusually brazen and threatening’, with the hackers’ message demanding the company engage with them or they will leak whatever they claim to have obtained.
In a statement shared with LADbible, he said: “The attackers aren’t simply claiming to have breached ASOS – they’re publicly telling the company to engage with them or they will leak what they say they have obtained.
It is not known who is behind the hack (Jakub Porzycki/NurPhoto via Getty Images)
“What makes it even more concerning is how that threat appears to have been delivered. A message apparently written for ASOS’s data protection and IT teams has instead been pushed directly to customers through the company’s own app notification system.
“That suggests someone has gained unauthorised access to at least part of ASOS’s systems, although we don’t yet know how extensive that access is.”
He went on to explain that customers should be alerted to emails and texts going forward, adding: “What customers should be particularly alert to now is what happens next.
“High-profile cyber incidents create ideal conditions for phishing attacks.
“Criminals may exploit the publicity by sending emails and texts claiming to be from ASOS, perhaps asking customers to reset a password, confirm payment details, check an order or claim a refund.
“Don’t click links in unexpected messages, even if they look convincing. Go directly to the ASOS app or website instead.
“Customers should also make sure their ASOS password is unique and, if they’ve used the same password elsewhere, change it on those accounts too.
“Until ASOS completes its investigation, we won’t know exactly what has been accessed or how the attackers got in. But this incident shows how powerful access to a trusted communications channel can be.
“When an attacker can potentially speak to customers through a company’s own systems, it makes the threat considerably more convincing and potentially much more damaging.”
Rhythm Superfoods Kale Chips, Zesty Nacho, Organic and Non-GMO, 2.0 Oz (Pack of 4), Vegan/Gluten-Free Superfood Snacks
(as of October 7, 2026 00:56 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
RIVER OF GOODS LED Boho Ceiling Fan with Hand Woven Brown/Natural Rope - Macrame Knot Work and Hemp Rope Style Eclectic Cottage Decor - 52" L x 52" W - Rich Barnwood/Light Driftwood Fan Blades
(as of October 7, 2026 00:56 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
Supa Ant Fire Blanket -Certified 1500F Extra Thick, Glow in The Dark | Fireproof Emergency Supplies. 500gsm, 0.5mm Thick Fire Blankets Emergency For Home. 5pc Fire Safety Emergency Blanket 40"x40"
$92.95 (as of October 7, 2026 00:56 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
RIVER OF GOODS Stained Glass Bird Accent Lamp - 8" W x 13.5" H - Tiffany Style Table Lamps for Home, Office Desk, Bedroom, Nightstand - Blue Jay Decor
(as of October 7, 2026 00:56 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)




Post Comment