Global Internet in Turmoil: Shocking AI Warning Triggers Massive Website Blackout and Unleashes Untold Cyberattack Wave
So, imagine this: you’re cruising the web, sipping your coffee, maybe catching up on the latest memes, when suddenly—bam! Thirty-two UK government websites suddenly vanish like your Wi-Fi signal in a dead zone. All because of a gargantuan security flaw in PHP, the backbone of more than 75% of the internet’s websites. Yeah, that huge. Now, here’s the kicker: this isn’t just any vulnerability, but one dubbed the “most severe ever discovered” by yours truly—AI. Crazy, right? It’s like finding out the foundation of your dream house has termites, and the exterminator’s still stuck in traffic. Now everyone’s scrambling, hacking attempts are pouring in by the millions, and officials are urging site owners to either patch up or shut down temporarily. So, are we witnessing the digital equivalent of a city-wide blackout—or just a harsh reminder that even the internet can catch a cold? Buckle up, ’cause it’s a wild ride. LEARN MORE
Internet users have for days been warned about major security flaws described as the ‘most severe vulnerabilities ever discovered’ by AI.
And now, thirty-two UK Government services are offline while work is carried out to address cybersecurity issues.
Throughout Thursday (22 October), organisations globally have been scrambling to fix a critical security flaw in the programming language PHP used by the majority of websites.
The vulnerabilities lie within PHP, which has been used internationally since the 2000s to build websites.
It’s estimated that it powers more than 75 percent of all websites on the internet, meaning the server outage could impact millions of sites across major platforms and social media.
Site operators have now been urged to install a new emergency fix or consider taking their platforms offline.
Greg Brockman, the president of OpenAI, said in an X post that hackers could exploit the vulnerability to steal private user data or modify websites.
Internet users are facing difficulty using some sites (Getty Stock)
‘Millions’ of hacking attempts
The PHP security issue identified could allow attackers to remotely control any web servers running PHP. Many attempts at exploiting the vulnerability were spotted within hours of it being announced, according to Amazon and Cloudfare.
Cloudfare chief executive Matthew Prince said on Thursday the firm spotted hundreds of thousands of hacking attempts within two hours of the announcement, with millions now ongoing.
“We consider this one of the most impactful security issues in recent memory,” OpenAI described in a blog post.
Downing Street on Thursday said no large UK public-facing critical services have been affected, but some ‘limited’ Government websites have gone dark while issues are resolved.
National Cyber Security Centre (NCSC) experts are working with OpenAI, whose technology was used to discover the vulnerabilities, and partners around the globe to address potential problems, a No 10 spokesperson said.
Websites globally are affected (Getty Stock)
Developers warned of ‘critical’ issue
The development comes after cybersecurity chiefs warned UK organisations on Wednesday that a ‘critical security issue’ had been discovered in PHP, which is used by almost 70 percent of websites according cybersecurity firm Cloudflare.
A Downing Street spokeswoman told reporters: “Work has already taken place across Government to identify and fix potential exposures to our systems, and our experts are continuing to work closely with both OpenAI and international partners on this issue.
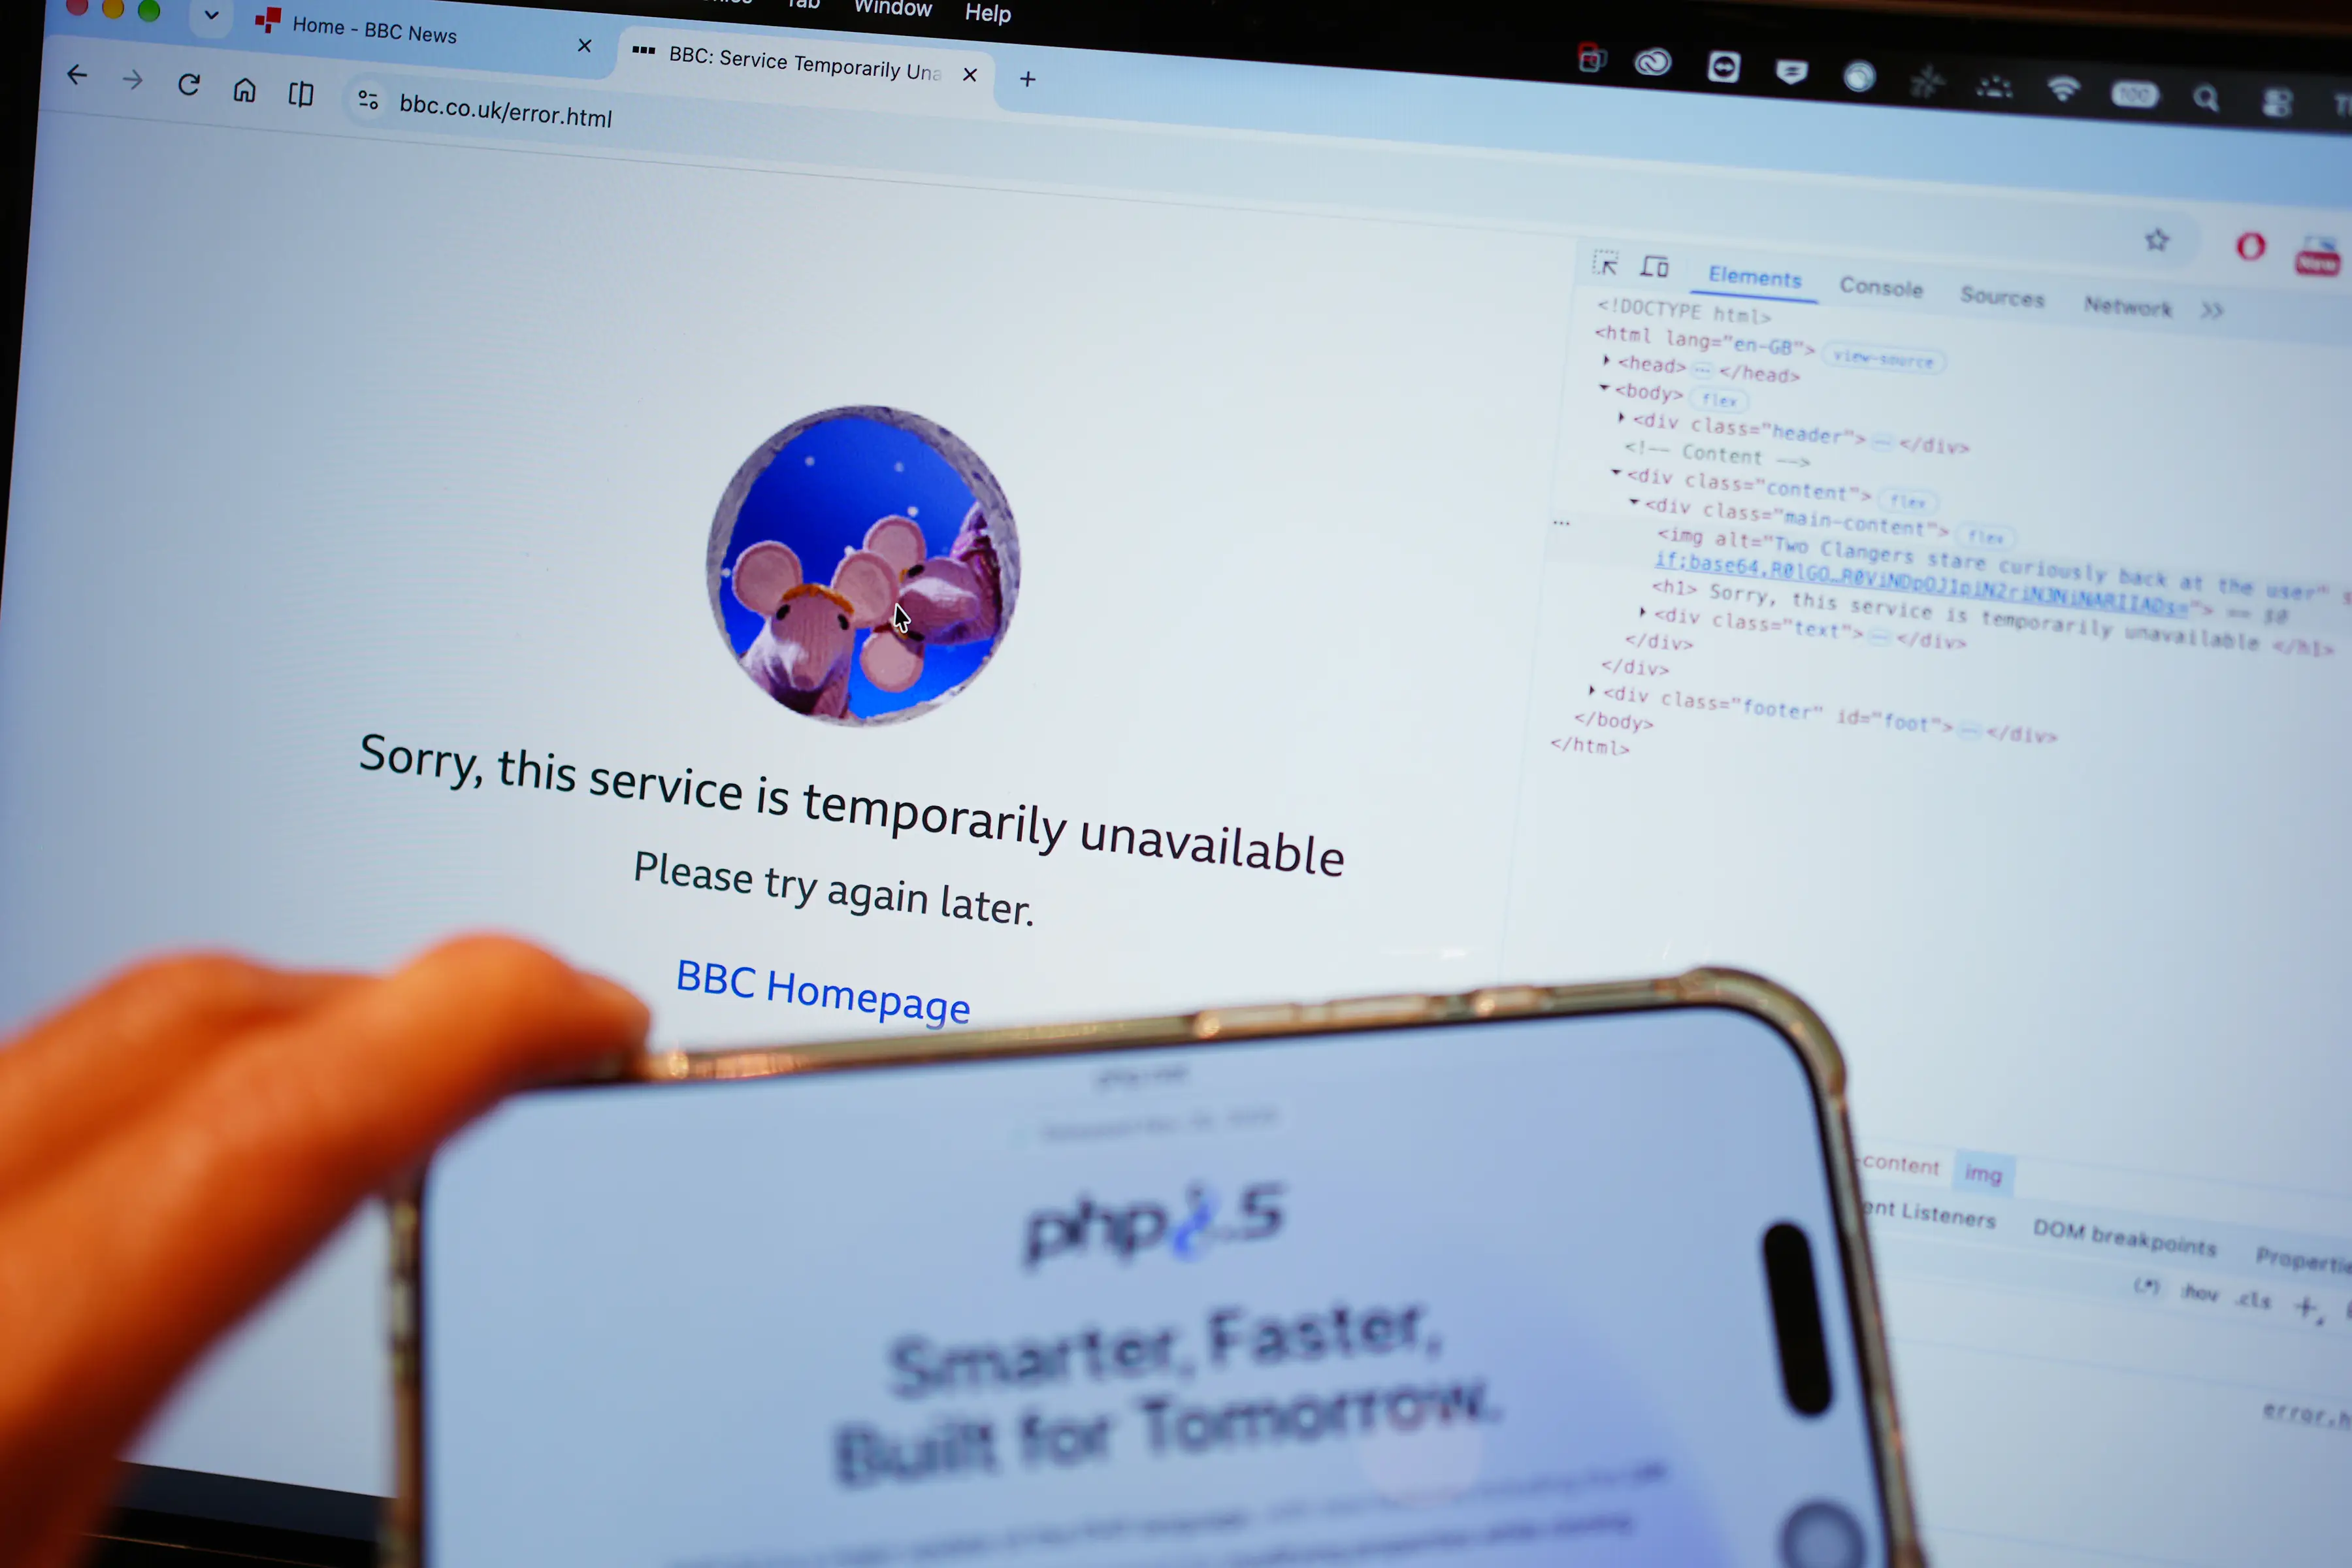
Pages were unavailable online (Yui Mok/Press Association)
“No large public-facing critical services are being affected by the exercise, but some limited services may temporarily be offline while security work is carried out.
“But this does not mean they were hacked, and work continues to resolve any issues.”
Organisations have been urged by the NCSC to update to a new, fixed version of the PHP software – or consider taking their websites offline if they cannot be upgraded immediately.
PHP developers had reportedly planned a security update on Thursday, but the release was brought forward after details of its work to address the vulnerabilities leaked online.
Alan Woodward, a visiting computer science professor at the Surrey Centre for Cyber Security (SCCS), said the vulnerability had in fact already been identified by human researchers in 2024, but it was then believed exploiting this security flaw would be “too complicated”, and nothing was done.
“The cat was let out of the bag rather earlier than it was supposed to have been”, he said.
“There’s always a window between the flaw being publicly known about and it being patched so that the attackers can’t successfully get in.
“And what happened, unfortunately, the day before the patch was out, somebody let the cat out of the bag.
“There was an initial version of the patch that was released, and so it was very easy to compare the original with the patched version and see which bit of code you needed to go and exploit.”
Joking Hazard by Cyanide & Happiness - 360+ Funny & Inappropriate Comic Cards, Hilarious Party Games | Includes Add-Your-Own-Words Cards
$24.95 (as of October 23, 2026 01:01 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
RIVER OF GOODS Coastal 52 Inch Wooden Bead LED Ceiling Fan, Brown
(as of October 23, 2026 01:01 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
1MORE Triple Driver in-Ear Earphones Hi-Res Headphones with High Resolution, Bass Driven Sound, MEMS Mic, in-Line Remote, High Fidelity for Smartphones/PC/Tablet - Silver
$61.59 (as of October 23, 2026 01:01 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)
Skater Trainer Wheels - Beginners get Skateboard Tricks Fast, Safe and Fun | Viral accessory gift - Helps beginners stay excited about their new skateboard - Kids & parents love these
$25.95 (as of October 23, 2026 01:01 GMT +00:00 - More infoProduct prices and availability are accurate as of the date/time indicated and are subject to change. Any price and availability information displayed on [relevant Amazon Site(s), as applicable] at the time of purchase will apply to the purchase of this product.)




Post Comment